¿Esta web tiene virus? Cómo saber si una página es segura antes de entrar
Comprueba en un minuto si una web tiene virus antes de entrar, qué significa cada aviso de Chrome o Edge y qué hacer si ya metiste…
Leer la guía →Analizamos tu web desde fuera —cloaking, malware, ficheros expuestos, listas negras y reputación— y, si hace falta, la limpiamos y la vigilamos 24/7. Para pymes, e-commerce y entornos exigentes como la banca.
Escaneo gratuito, sin instalar nada. También informe profundo, limpieza y SOC gestionado 24/7.
PathSentinel is the professional identity of Jesús Macías: a technology entrepreneur and cybersecurity student building a serious profile around secure cloud architecture, operational resilience, AI-assisted threat intelligence, routing-aware security and business systems that can be governed and recovered.
AWS-first architecture, IAM, VPC, logging, KMS, GuardDuty, Security Hub, hardening and recovery.
Infrastructure as Code, CI/CD, Docker, Ansible, Terraform/OpenTofu, GitHub/Jenkins, rollback and controlled delivery.
Continuity, evidence, documentation, backups, restore tests and reduced dependency on heroic memory.
BGP, ASN, DNS, routing, OSINT, anonymity networks and adversarial infrastructure context.
Signals, RAG, prioritization, evidence, playbooks and human-supervised operational actions.
Attack-informed defense: validate controls, detect paths, improve architecture and document response.
ISO 27001, NIS2, CIS Controls, audit trails, policies, legal/fiscal evidence and operational proof.
Radar CTI, papers, portfolio, university projects and production systems turned into public knowledge.
The objective is not to look modern. The objective is to know what matters, what can fail, how it can be attacked, how it can be detected and how it can be recovered.
{
  "observe": ["cloud", "identity", "network", "business"],
  "protect": ["access", "evidence", "delivery", "recovery"],
  "validate": ["controls", "logs", "backups", "attack_paths"],
  "goal": "turn business fragility into governable architecture"
}Collect signals from cloud, CTI, OSINT, systems, documents, endpoints and business processes.
Connect CVEs, assets, infrastructure, identity, routing, evidence and operational context.
Separate noise from risk and turn findings into actions, playbooks and controls.
Design for rollback, restore, continuity, documentation and reduced human dependency.
Comprueba en un minuto si una web tiene virus antes de entrar, qué significa cada aviso de Chrome o Edge y qué hacer si ya metiste…
Leer la guía →The attacker only needs to be right once; the defender, every time. The cognitive and emotional load behind each cybersecurity role (Red Team, DFIR, Purple Team)…
Leer la guía →El atacante solo necesita acertar una vez; el defensor, todas. Qué desgaste cognitivo y emocional sufre cada rol de ciberseguridad (Red Team, DFIR, Purple Team) y…
Leer la guía →Comprueba en un minuto si una web tiene virus antes de entrar, qué significa cada aviso de Chrome o Edge y qué hacer si ya metiste tus datos o tu tarjeta.
El atacante solo necesita acertar una vez; el defensor, todas. Qué desgaste cognitivo y emocional sufre cada rol de ciberseguridad (Red Team,…
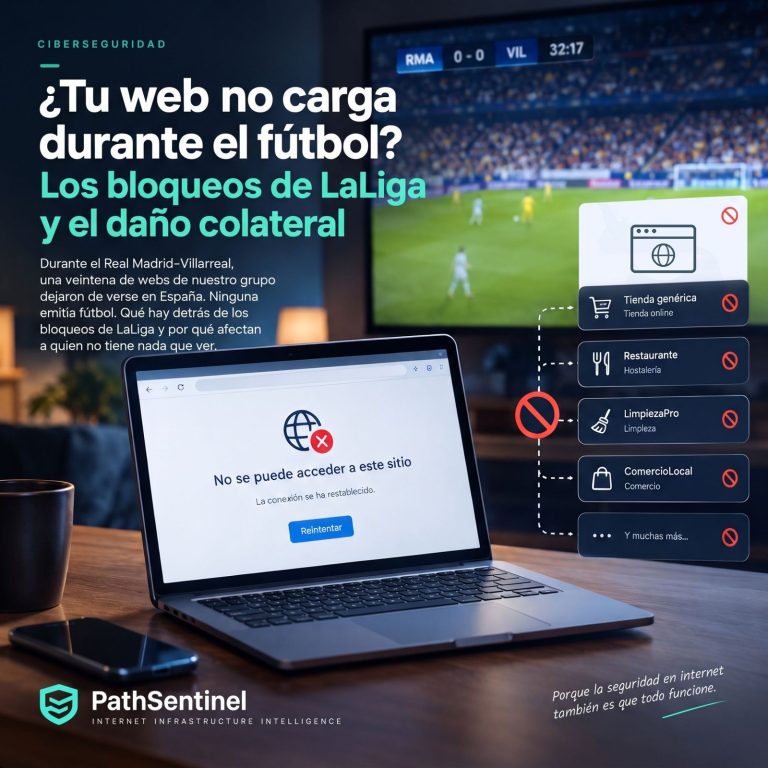
Bloqueos de LaLiga en noviembre de 2026: por qué caen webs legítimas en los partidos, cómo comprobar si te afecta hoy y…
Señales de que tu web tiene virus aunque tu antivirus no lo vea, cómo comprobarlo gratis sin instalar nada y qué hacer…
Nuestras tres guías clave — de saber si estás comprometido a recuperarte de un incidente.
De comprobar si estás comprometido a vigilar y responder 24/7.
Seguridad Online — nuestra publicación abierta sobre seguridad web, RGPD y plugins de WordPress para pymes. Editada por PathSentinel: ver la revista · índice completo
Vulnerabilidades en plugins de WordPress · Protección de datos y ciberseguridad para pymes · Configuración segura de una web